

More than a quarter of maritime suppliers have been identified as having ‘high’ or ‘very high’ cyber vulnerabilities, according to new data released by Achilles Network.
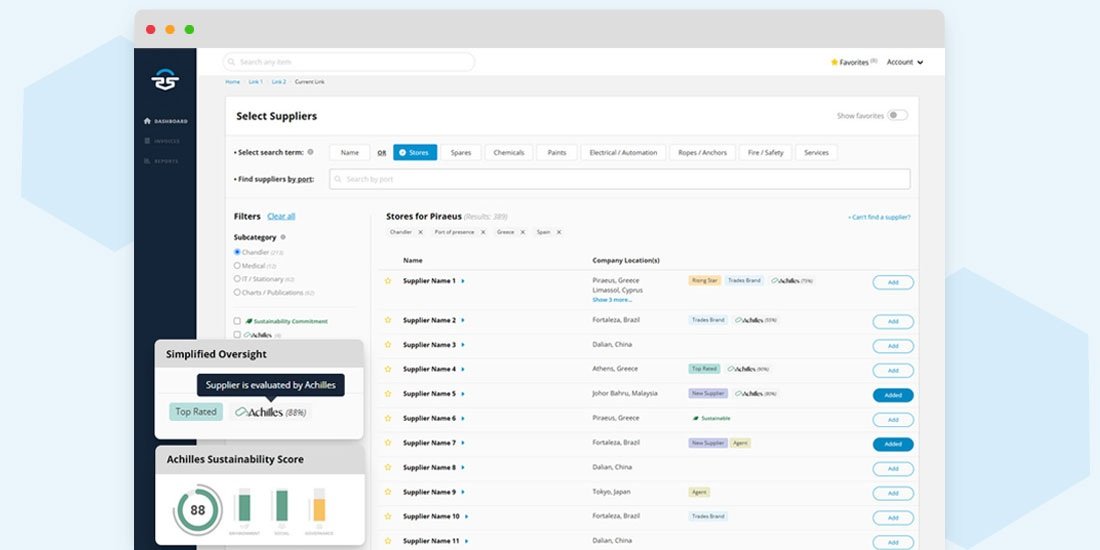
The findings come as maritime procurement platform Procureship’s integration with Achilles goes live, enabling shipowners and operators to view verified ESG and cybersecurity indicators directly within their procurement workflows.
More than 1,000 global maritime suppliers were assessed over a 12-month period by the partners, with 28% found to have elevated cyber risk levels. The review also showed that over half lacked third-party-assured anti-bribery systems, information security policies, or public liability insurance.
Around a quarter of suppliers had not yet measured their greenhouse gas emissions, the companies note, while more than half used uncertified carbon systems.
Despite this, nearly half of those reviewed were found to have certified environmental management systems in place, and 13% had developed formal decarbonisation plans.
“Shipping companies are increasingly using data-driven insights to target greater supplier relations and address their own environmental and cyber vulnerabilities,” said Craig Rodgerson, CEO of Achilles.
“By embedding this type of data into the Procureship platform, users are able to gain early warnings of potential supplier vulnerabilities, enabling them to shift their risk management from reactive to predictive.”


